Can a tool connection setting run code?
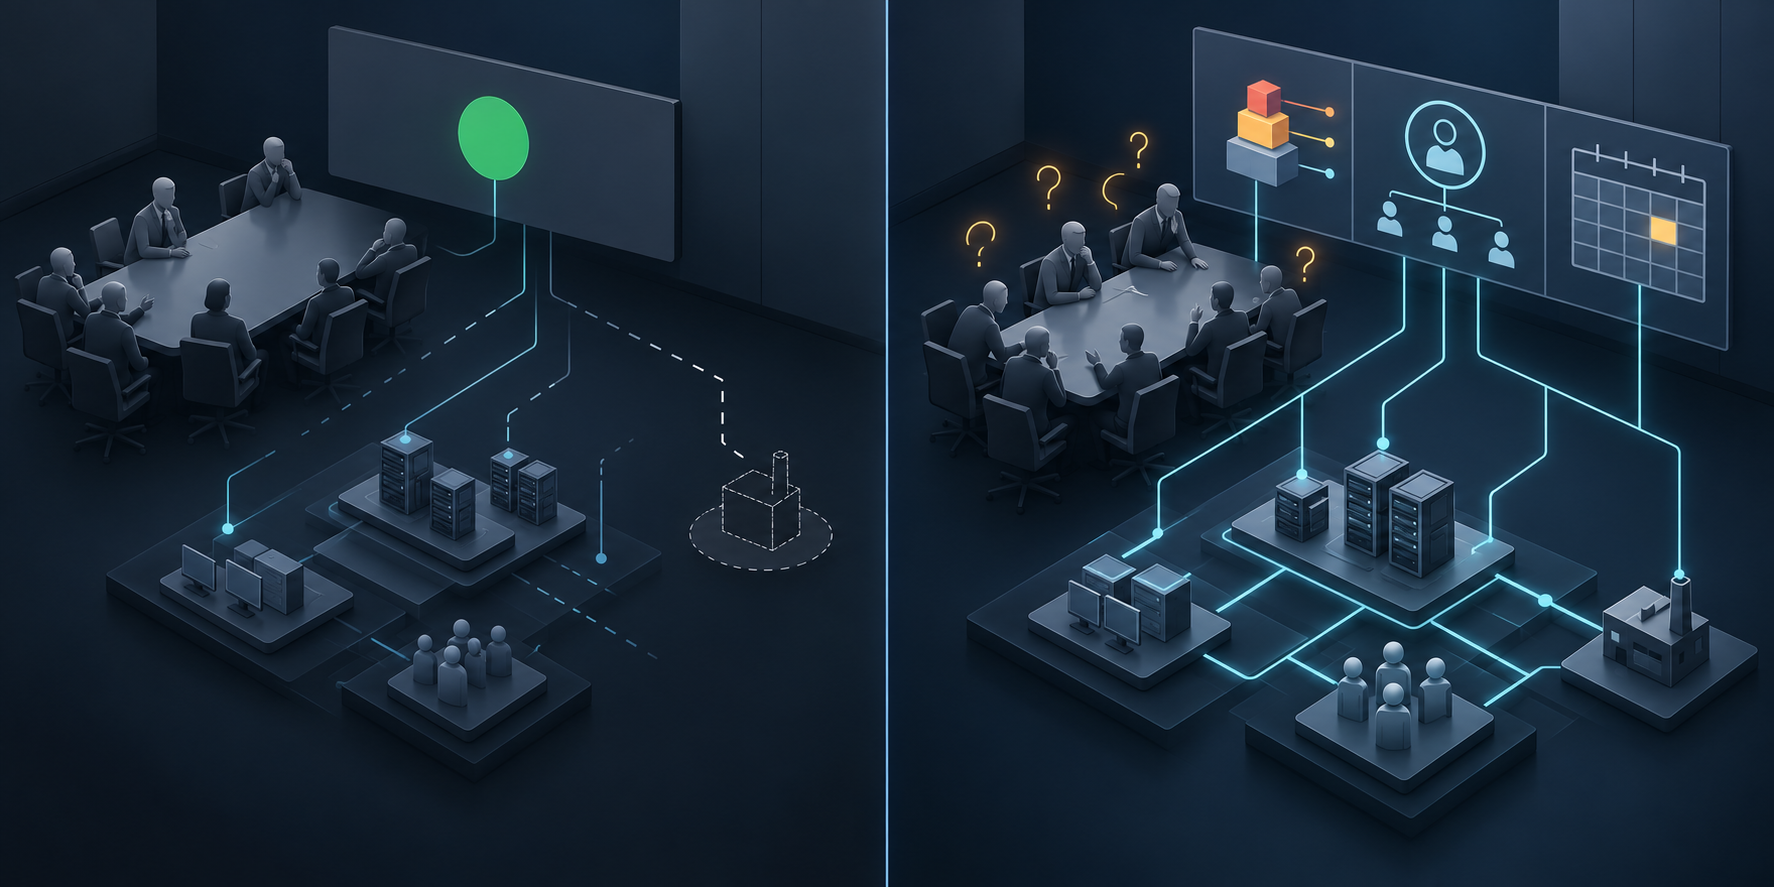
When you connect an AI agent to a tool, are you just filling in a form, or are you telling a server which program to run? Langflow is a tool for building AI agents and workflows. For one type of connection, the answer turned out to be the second.
MCP (Model Context Protocol) connects AI applications to outside tools and data. With the stdio transport, the MCP server is a local program that the host launches and talks to through standard input and output. So setting up a stdio connection means naming a command for the host to run. If anyone who can edit that setting can name any command, the setting becomes a remote control for the server.
What did the first advisory describe?
On 10 September 2026, Langflow published advisory GHSA-7w94-79vh-5mr2. It was rated Critical, with a CVSS score of 9.9 out of 10. It described remote code execution, meaning someone could make the server run commands they chose. Any authenticated user, not only administrators, could add a stdio MCP server. Its command went to a shell with no validation, no allowlist and no sandboxing. The advisory lists 1.9.0 as the patched version.
The command ran every time the server list loaded, so a stored configuration could fire again whenever someone opened the MCP settings page, administrators included. These configurations lived in project settings, so normal flow review did not show them. The weakness is classified as CWE-78, OS command injection: outside input shapes an operating-system command.
Why wasn't the first fix the end?
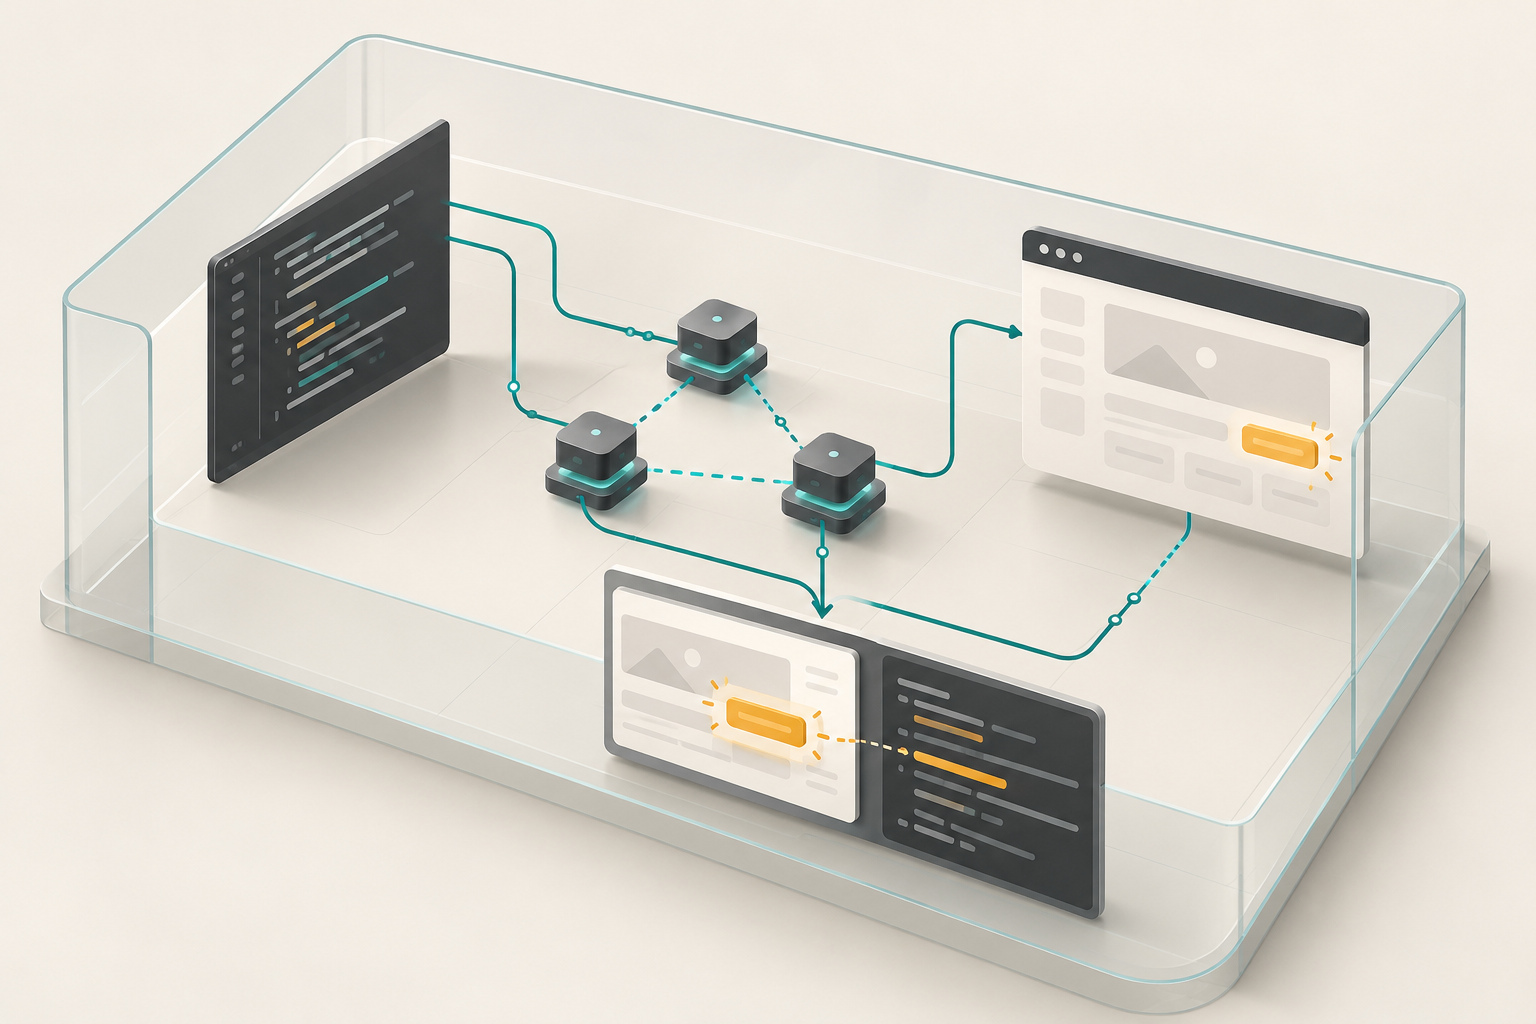
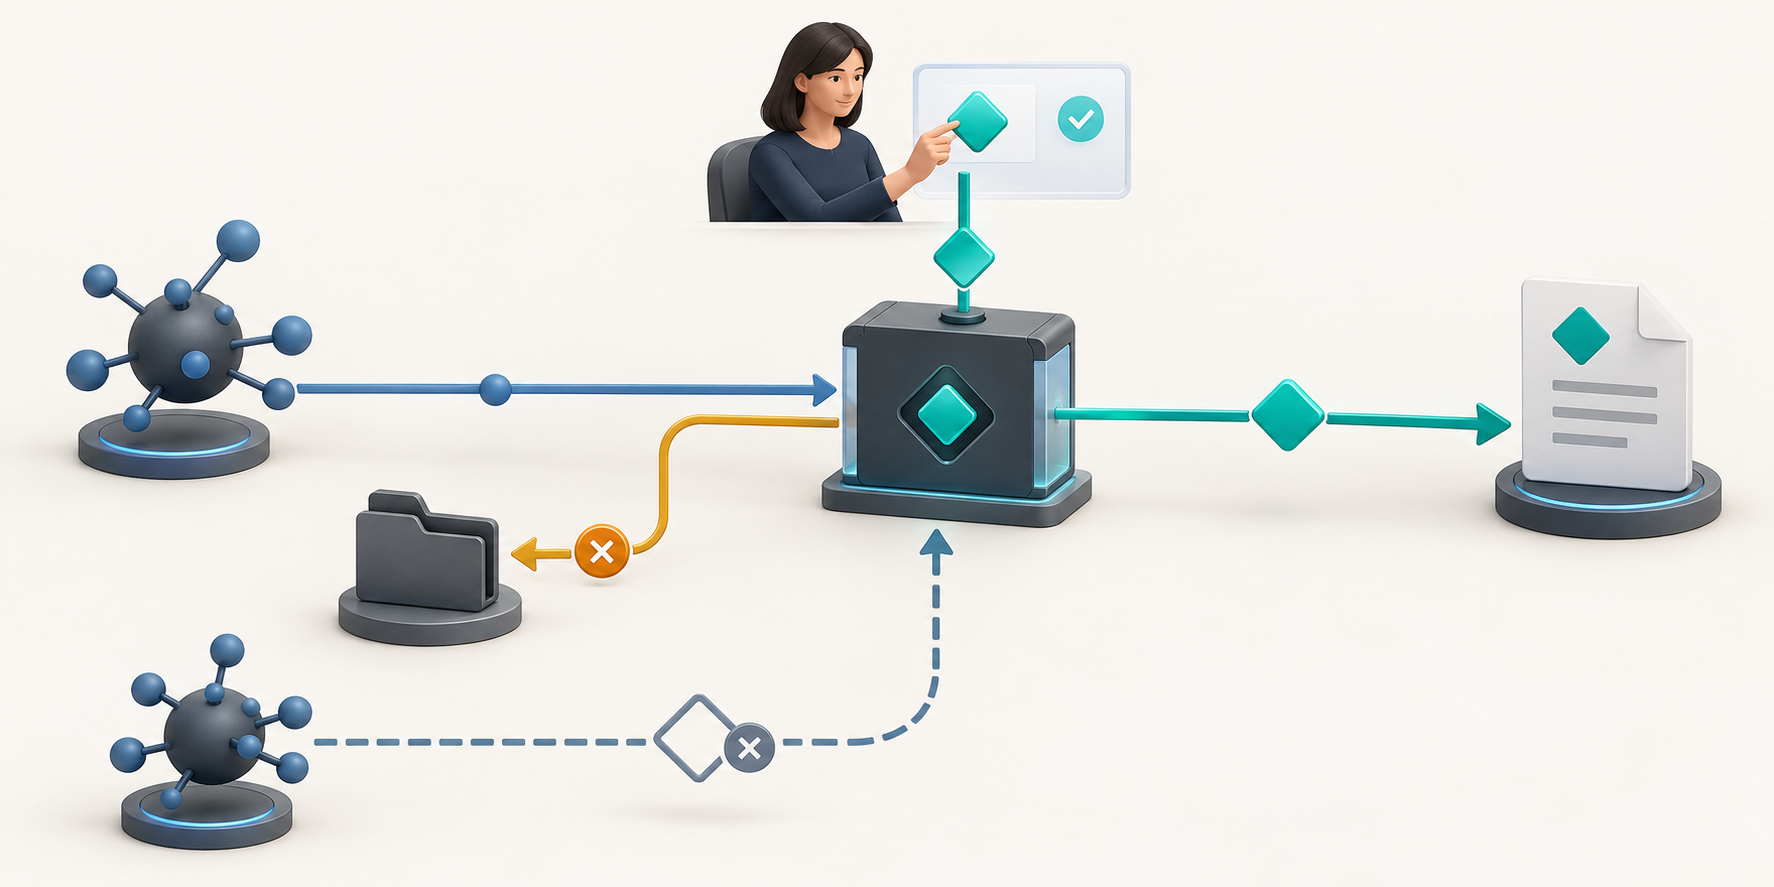
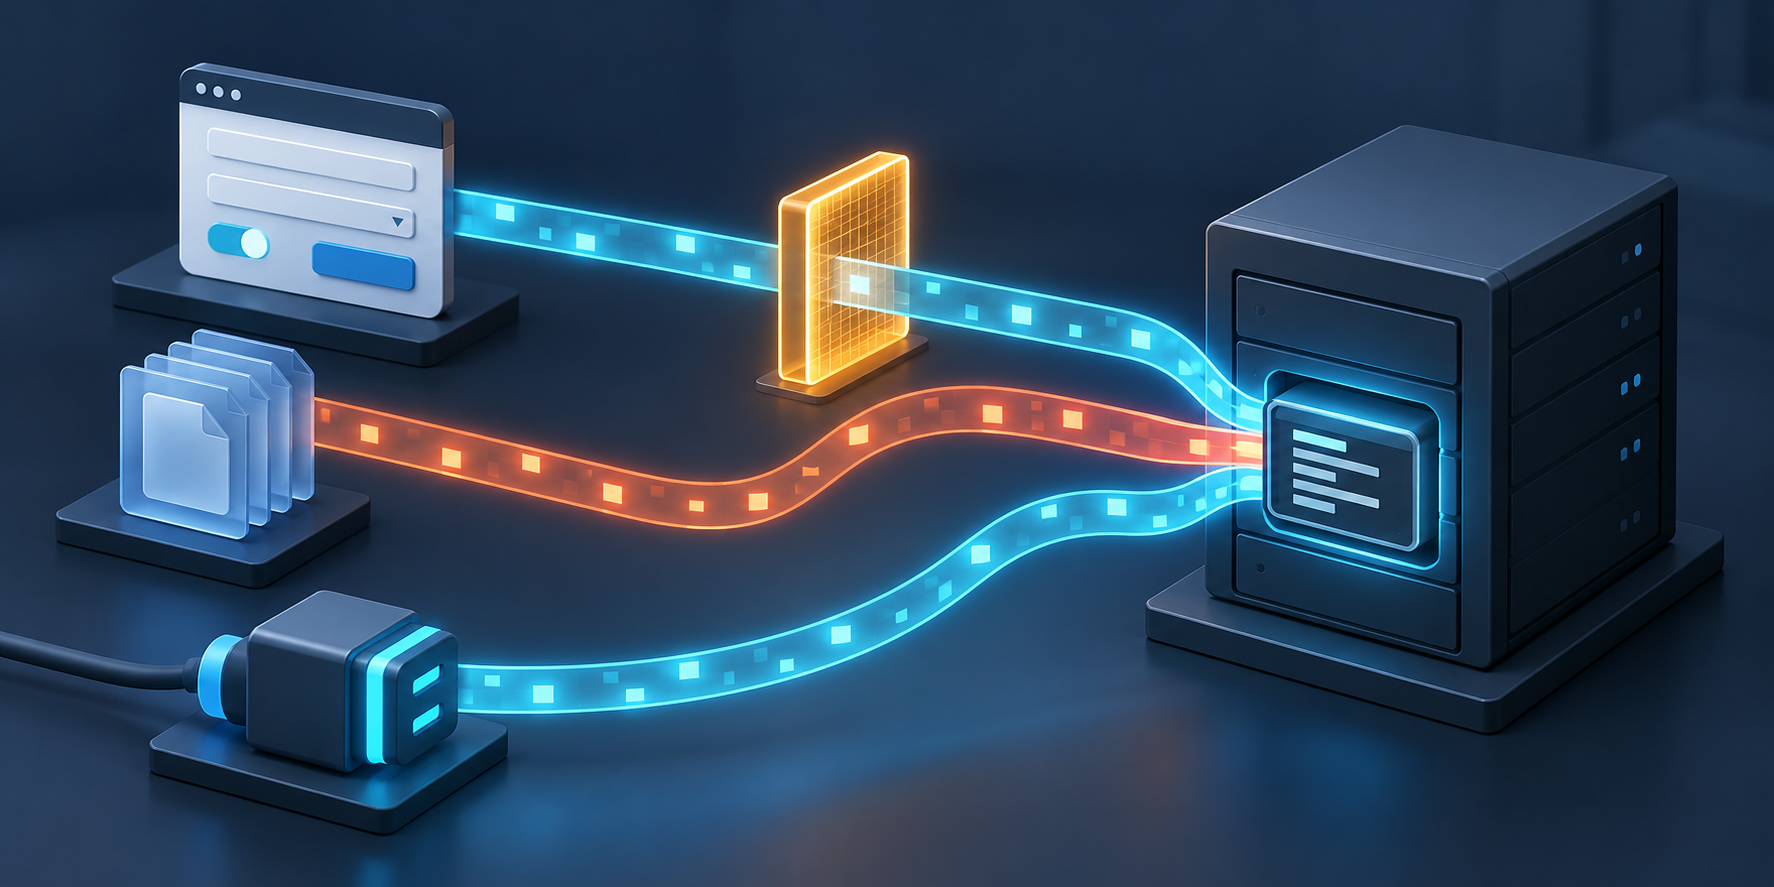
On 28 September 2026, a second advisory, GHSA-w794-rj3p-xv45, covered versions from 1.1.2 up to but not including 1.10.3. It explained that the fix came in two steps. The first step added a command allowlist and argument and environment checks to the settings API's data model. But the code that actually launched the process still had no validation and still used a shell. A configuration could arrive another way, for example as an MCP Tools component value embedded in a flow. Then it never passed through those checks and could still run arbitrary commands.
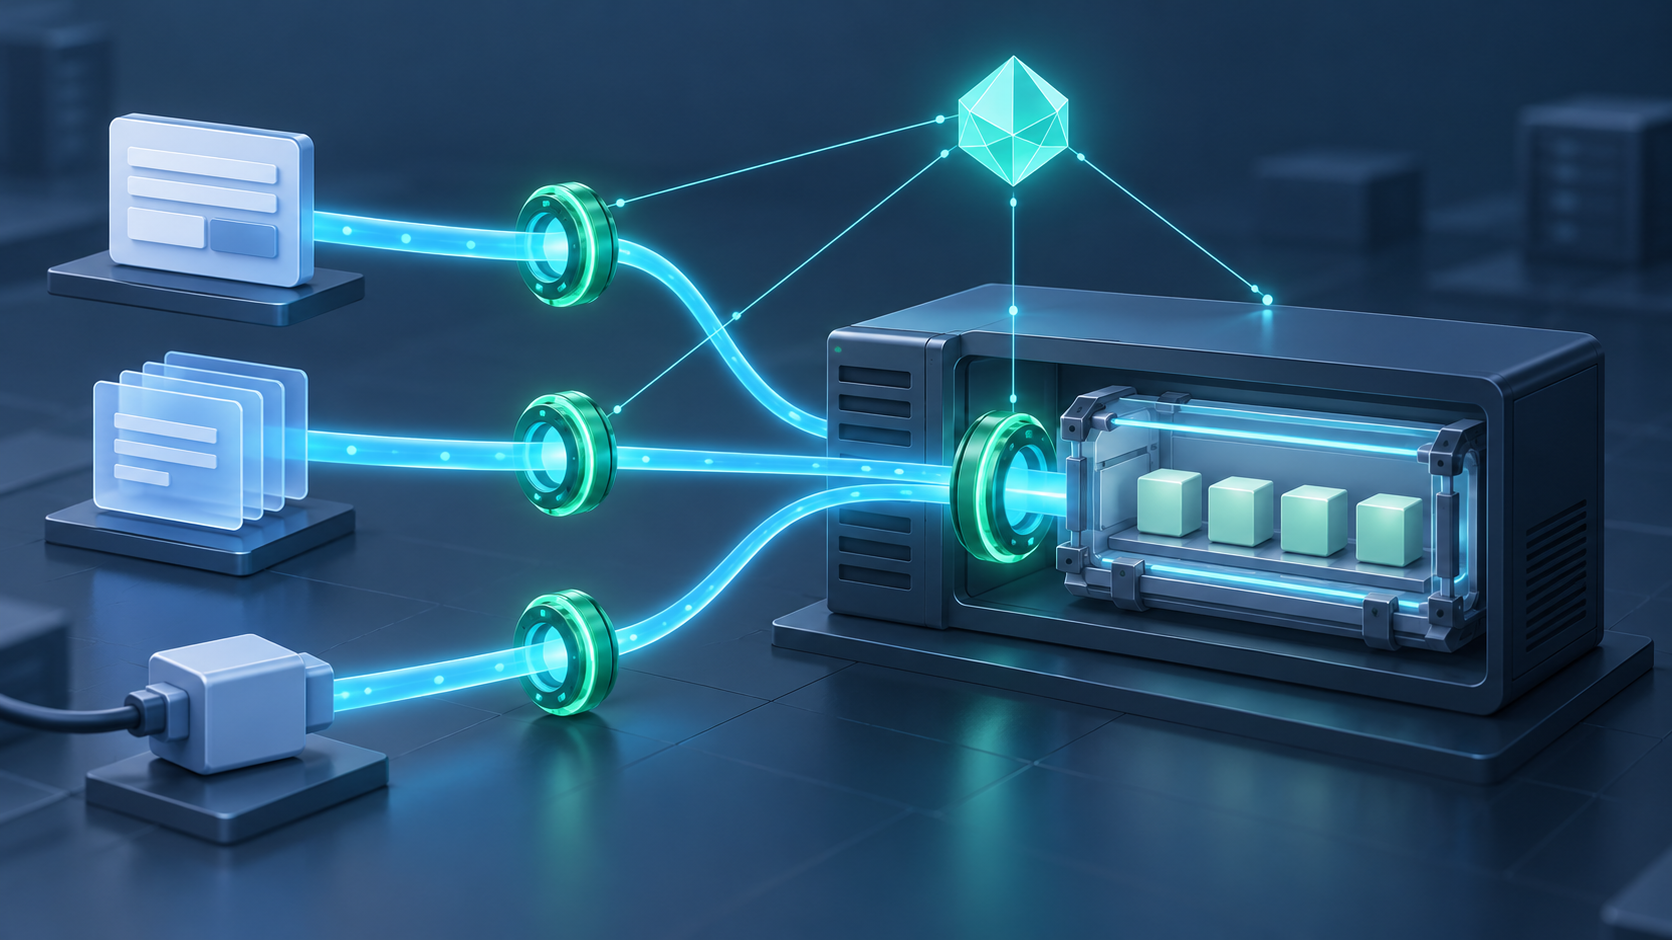
Picture a guard at the front desk while the loading dock stays unlocked. Version 1.10.3 changed the design: one shared policy enforced at the API, at flow execution and right before the process starts, with no shell. The advisory also notes that the command ran before any MCP handshake. That is why it could execute even when the interface reported that the server had failed to start.
A hypothetical example
In this hypothetical example, a team upgrades to a release that contains only the first fix. They confirm that the settings page now rejects unfamiliar commands and conclude the issue is closed. Later, someone imports a shared flow that carries its own MCP tool configuration. That configuration never touches the settings form, so the check the team tested never sees it. The test was real. It just covered only one way in.
What can defenders take from it?
The second advisory supports a few practical steps:
– Run 1.10.3 or later. The advisory describes the issue as fully fixed there and in 1.11.0+.
– Disable LANGFLOW_AUTO_LOGIN, which defaults to true. It hands out a token without credentials and is documented as a development-only setting.
– Do not expose Langflow directly to untrusted networks, and give accounts only to trusted users.
– On multi-tenant deployments (one installation shared by several separate users or groups), consider the hardening settings the advisory lists, such as LANGFLOW_MCP_SERVER_ALLOWED_PACKAGES, which names exactly which packages may run.
Where should you look next?
When you review a fix for an injection flaw, a useful question is where the dangerous action finally happens, and whether the check sits there too. A protected form can still leave other routes to the same command. A concrete next step: list every Langflow instance you run, note its version and whether auto-login is on, and review its stored MCP server configurations for commands nobody recognises. The first advisory showed that these configurations persist and stay hidden from normal flow review.
References
- Authenticated RCE via MCP Stdio transport allows any user to execute arbitrary OS commands on the server · Advisory · langflow-ai/langflow · GitHub pip
- Langflow < 1.10.3: OS command injection (RCE) via arbitrary command in MCP stdio server configuration · Advisory · langflow-ai/langflow · GitHub pip pip pip