Skip to content

Cybersecurity Curious Posts

Who Can Accept Cyber Risk? Understanding Decision Accountability

1. Start with the decision, then identify the authority

Who can accept cyber risk? Editorial answer: a person or body whose assigned authority covers the consequences of that decision. A cybersecurity assessment informs the choice, but expertise alone does not establish approval authority. NIST Cybersecurity Framework (CSF) 2.0 provides a useful foundation: its Govern function addresses risk tolerances, roles, responsibilities, and alignment with enterprise risk management. These concepts help frame the question without supplying a universal approval hierarchy. [2]

NIST released CSF 2.0 on February 26, 2024, adding Govern to Identify, Protect, Detect, Respond, and Recover. NIST explains that cybersecurity belongs alongside other enterprise risks, including financial and reputational concerns. This article takes an evergreen educational angle rather than reporting a recent change. The recommendations below are editorial applications of those governance concepts; they are not a prescribed NIST approval procedure. [1]

2. Separate acceptance, tolerance, and assessment

NIST lists acceptance among possible risk responses, alongside mitigation, transfer, and avoidance. It connects the choice of response with potential effects on critical service delivery. Working explanation for this article: cyber risk acceptance is a decision to tolerate an identified cybersecurity exposure. This is an editorial explanation, not a formal NIST definition. Acceptance describes the chosen response; it does not demonstrate that the exposure has been reduced. [2]

NIST also explains that understanding risk tolerance helps organizations prioritize cybersecurity activities and spending. Working distinction for this article: tolerance provides the context for judging what exposure is bearable, while acceptance concerns a particular exposure. Assessment supplies information for that judgment. Keeping these ideas separate helps readers distinguish an explanation of possible harm from the authority to decide whether that harm is tolerable. [2]

Editorial recommendation: begin an acceptance discussion with the affected outcome, possible consequences, and important uncertainties. Then explain how the proposed response relates to organizational priorities and tolerance. A risk rating can support that discussion, but a rating without a consequence statement leaves the decision difficult to interpret. NIST's guidance supports prioritization according to mission requirements, risk tolerances, and resources rather than a single universal threshold. [2]

3. Match authority to the consequences

NIST describes the CSF as applicable across organizational levels and most effective within broader enterprise risk management. It also explains how senior leaders can use the framework to understand, direct, and manage cybersecurity risk. Editorial reasoning: the relevant authority should therefore be considered in relation to the activities and consequences affected, rather than inferred solely from who identified the technical concern. [2]

Editorial recommendation: distinguish three contributions to the discussion. The assessor explains the exposure and uncertainty. Someone responsible for the affected activity explains the operational consequences. The authorized decision maker considers the response against priorities, tolerance, and available resources. These contributions may overlap, but identifying them makes missing information easier to recognize. This allocation is a suggested discussion structure, not a requirement for particular job titles or separate individuals. [2]

Editorial reasoning: the breadth of the consequences matters. An assessment focused on one activity may overlook effects on other activities, shared resources, or organizational objectives. Where those effects extend beyond a proposed decision maker's remit, the approval arrangement needs to address that wider scope. This follows NIST's emphasis on enterprise risk; it does not establish that every acceptance requires a board decision or an executive signature. [1] [2]

4. Hypothetical example: a recovery gap

Hypothetical example: a generic organization wants appointment scheduling to resume by the next working morning after a cyber disruption. Its hypothetical assessment indicates that recovery could instead take several working days. During that period, appointments could be missed and rescheduling could become difficult. All details are invented for illustration. The example connects a cybersecurity recovery concern with an understandable consequence for an activity. [2]

In this hypothetical example, the desired recovery outcome and assessed capability differ. NIST's Current and Target Profiles offer a way to describe such differences: a Current Profile identifies outcomes being achieved, while a Target Profile describes desired outcomes. Comparing them can reveal gaps and support prioritization. Editorial reasoning: making the gap visible helps define the decision, but the comparison alone does not establish that acceptance is appropriate. [2]

Continuing the hypothetical example: the assessor explains the recovery estimate and its uncertainty, while the person responsible for appointment delivery describes the disruption. An authorized decision maker then considers improvement options and the exposure that would remain if improvement were deferred. If acceptance is chosen, the next-morning objective remains unmet. Editorial reasoning: an acceptance decision should make that unresolved difference visible rather than present approval as evidence of improved recovery. [2]

5. Preserve the reasoning behind the choice

Editorial recommendation: retain a concise explanation of the affected outcome, assessment uncertainty, alternatives considered, chosen response, decision authority, and assumptions supporting the choice. These are suggested discussion prompts, not mandatory NIST record fields. Their purpose is to make the relationship between evidence and decision understandable. NIST supports communicating cybersecurity outcomes and expectations among leadership, operational personnel, and other stakeholders. [2]

In the hypothetical scheduling example, that explanation would connect the recovery delay with appointment disruption and state why the authorized decision maker considers the remaining exposure tolerable. Editorial reasoning: it should also distinguish the desired improvement from what is currently achievable. That distinction gives a later reviewer something concrete to reconsider: the consequence, the response options, or the assumptions may change even when the recorded approval remains the same. [2]

6. Keep framework guidance separate from legal obligations

CSF 2.0 is cybersecurity risk guidance from NIST, a United States public institution. NIST states that it is not a regulatory agency and that most organizations use the framework voluntarily. The CSF sets out outcomes without prescribing a universal process for achieving them. Its international use does not create a shared legal rule about who may accept cyber risk, and using it does not guarantee compliance. [1] [2]

NIST explains that cybersecurity objectives may reflect applicable laws, rules, and regulations, and that Govern includes understanding and managing legal, regulatory, and contractual requirements. Editorial recommendation: consider those requirements before treating acceptance as an available response. This article makes no jurisdiction-specific legal determination and assigns no statutory approval duty. A governance decision and a determination that applicable obligations have been satisfied answer different questions. [2]

7. Reconsider decisions when their basis changes

NIST describes the six CSF functions as concurrent and continuous. It also explains that Target Profiles consider anticipated changes, including new requirements, technology adoption, and threat information. Editorial recommendation: connect review of an acceptance decision to changes in its supporting assumptions. Useful questions include whether the assessed consequences remain credible, whether uncertainty has increased, and whether the chosen response still fits organizational priorities. [2]

Returning to the hypothetical scheduling example: greater dependence on appointments, a longer recovery estimate, or a newly feasible improvement could prompt reconsideration. These are invented review triggers, not NIST thresholds. Editorial reasoning: review becomes more useful when it asks what has changed in the decision's basis. Repeating the original approval without examining that basis would provide little insight into whether the exposure remains tolerable. [2]

References

  1. NIST Releases Version 2.0 of Landmark Cybersecurity Framework | NIST Lock (checked 2026-10-14)
  2. Frequently Asked Questions | NIST Lock (checked 2026-10-14)

Educational content; verify applicable requirements with the relevant primary sources.

Comments closed
What is Hashing?

In previous posts, I covered symmetric and asymmetric encryption. Both help protect information by making it unreadable without the correct key. Another term that often comes up alongside encryption is hashing. So, what is hashing, and where does it fit into cybersecurity?

Hashing Basics

Hashing takes an input, such as a message or a file, and calculates a value called a hash or digest. With an algorithm such as SHA-256, the output has a fixed length regardless of whether the input is a short sentence or a large download.

Think of it as a digital fingerprint. You can compare fingerprints to help check whether data has changed, without comparing every part of the original files yourself.

The same input produces the same hash when the same algorithm is used. Even a small change, such as replacing one letter, will usually produce a very different result. Secure cryptographic hash functions are also designed to make it impractical to recover an input from its hash or deliberately find two different inputs with the same hash. Such a matching pair is called a collision.

Hashing vs. Encryption

The main difference is their purpose:

  • Encryption protects confidentiality. Someone with the correct key can decrypt the information and read it again.
  • Hashing produces a digest for comparison. There is no decryption key that turns the hash back into the original message.

However, this does not mean that hashing makes a weak password impossible to discover. An attacker can hash likely guesses and compare the results.

Example Use Case: Checking a Download

Imagine you download a software installer and the publisher provides its SHA-256 hash.

  1. Download the file from the publisher’s official website.
  2. Calculate the SHA-256 hash of the downloaded file using a local tool.
  3. Compare your result with the hash published by the developer.

If the values differ, the file does not match the expected download. It may be incomplete, corrupted or modified.

A matching hash is only as trustworthy as the reference you compare it against. If an attacker replaces both the file and the published hash, that comparison alone will not expose the change. It also does not prove that the software itself is harmless.

How Does Hashing Help Protect Passwords?

A service should normally store a password hash rather than the password itself. When you sign in, the service uses a password verification function to check your entry against the stored result.

Password storage needs a dedicated algorithm, such as Argon2id, and a unique random salt for each password. A salt is stored alongside the hash and helps prevent identical passwords from producing identical stored results. Password hashing algorithms deliberately make guessing more expensive; a fast general-purpose hash such as SHA-256 alone is not suitable for storing passwords.

Why Does It Matter?

Hashing helps us check file integrity and is part of systems that verify passwords and digital signatures. It serves a different purpose from encryption, but both are useful building blocks for protecting information.

The next time you see a long SHA-256 value beside a download, you will know what it is there for: a way to compare the file you received with the file you expected.

Further Reading

Comments closed

What is CyScan.io


CyScan.io, also known as Cyber URL Scanner, is a simple online tool to check websites before you interact with them. Built by cybersecurity professionals, it does real-time scanning to detect threats hidden behind a link — malware, phishing traps or invasive tracking scripts.

With one click you get the full picture of a site’s safety — which is handy in today’s internet full of hidden dangers and deceptive links.


What is cool:

🔍 Real-Time URL Scanning

CyScan doesn’t give you a “safe/unsafe” score — it actively analyzes URLs to detect malicious code, phishing patterns, tracking technologies and other signs of risk. You get instant feedback so you can make smart decisions before clicking.

⚙️ No Setup Required

No account, no installation, no technical knowledge required. Just paste a link and get results. Whether you’re a developer, IT admin or casual user, this makes CyScan easy to integrate in your daily routine.

📊 Clean Reports

Results are presented in a simple way — no jargon, no PDFs. Just a summary of detected threats, categorized by severity, with details even non-techies can understand.

🧠 No Noise, Just What Matters

I really liked how focused and minimalistic CyScan’s reporting is. It doesn’t overwhelm you with technical data — just the essentials. You see what matters, and nothing more.


Who Should Use CyScan.io?

CyScan.io isn’t just for cybersecurity professionals. It’s useful for:

  • Individuals who want to check if a link is safe before clicking
  • Freelancers and web developers managing multiple websites
  • Digital agencies performing basic security hygiene for clients
  • Anyone who wants a quick and easy way to stay safe online

Final Thoughts:
CyScan.io isn’t a full-stack vulnerability scanner and it doesn’t pretend to be. But for quick and easy website safety checks it does exactly what it promises — and does it well. Whether you’re techy or not, it’s a tool to bookmark.

Comments closed

Asymmetric Encryption

Decrypt Everything: Understanding Asymmetric Encryption

Introduction:
In today’s digital world, protecting our data is crucial. Encryption plays a key role in keeping our sensitive information secure during transmission. Among the different encryption methods, asymmetric encryption stands out due to its unique approach and robust security features. So, what exactly is asymmetric encryption, and why is it so essential?

Encryption Basics:
Encryption is the process of transforming plain text into coded text, making it unreadable to unauthorized users. This ensures that only those with the correct key can decrypt and access the original information. There are two main types of encryption: symmetric and asymmetric. In symmetric encryption, the same key is used for both encryption and decryption. Asymmetric encryption, on the other hand, uses two keys: a private key and a public key.

What is Asymmetric Encryption?
Asymmetric encryption, also known as public-key cryptography, involves a pair of keys that are mathematically related: a public key and a private key. The public key is used to encrypt data, while the private key is used to decrypt it. The public key can be shared openly, but the private key must be kept secure. This ensures that even if someone intercepts the encrypted data, they cannot decrypt it without the private key.

How Does Asymmetric Encryption Work?
Here’s a simple breakdown of how asymmetric encryption works:

  1. Key Pair Generation: A pair of keys—a public key and a private key—is created.
  2. Public Key Distribution: The public key is shared with the intended recipient(s).
  3. Data Encryption: The sender encrypts the data using the recipient’s public key.
  4. Sending the Encrypted Data: The encrypted data is sent to the recipient over a secure channel.
  5. Data Decryption: The recipient uses their private key to decrypt the data and access the original information.

Example Use Case:
Imagine Alice wants to send Bob a private message. Bob shares his public key with Alice. Alice uses Bob’s public key to encrypt her message and then sends the encrypted message to Bob. Bob can then decrypt the message using his private key, ensuring that only he can read it.

Advantages of Asymmetric Encryption:
Asymmetric encryption offers several advantages over symmetric encryption:

  1. Enhanced Security: The use of two keys makes it more secure and harder for attackers to access the data.
  2. Public Key Distribution: Public keys can be shared widely without compromising the security of the private key.
  3. Digital Signatures: Asymmetric encryption enables digital signatures, which verify the authenticity and integrity of messages and documents.

Applications of Asymmetric Encryption:
Asymmetric encryption is used in various important applications:

  1. Secure Communications: Email encryption (e.g., Pretty Good Privacy, or PGP) uses asymmetric encryption to ensure message privacy.
  2. Digital Certificates and SSL/TLS: Protocols like SSL/TLS use asymmetric encryption to secure online transactions and communications.
  3. Blockchain and Cryptocurrency: Asymmetric encryption is crucial in blockchain technology and cryptocurrencies for securing and verifying transactions.

Challenges and Considerations:
While asymmetric encryption has many benefits, it also presents some challenges:

  1. Computational Demand: Asymmetric encryption requires more computational power than symmetric encryption, which can affect performance.
  2. Key Management: Safeguarding the private key is critical, as losing or compromising it can lead to data breaches.

Conclusion:
Asymmetric encryption is a fundamental component of modern cybersecurity. Understanding how it works and its various applications highlights its importance in protecting our digital world. As technology continues to evolve, asymmetric encryption will remain a vital tool in combating cyber threats, keeping our information safe and secure.

1 Comment

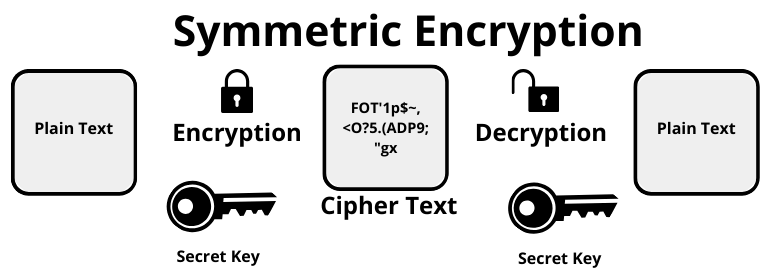
What is Symmetric Encryption?

Symmetric encryption is a method of protecting data by using a private key to encrypt (lock) and decrypt (unlock) it. Both the sender and recipient must possess this key, which could be a word, passphrase, or complex combination of characters, numbers, and symbols, to access encrypted information.

One advantage for organizations using this type of encryption is its cost-effectiveness. However, it does come with certain drawbacks. In symmetric encryption, keys can remain usable indefinitely, leading organizations to simply forget to perform periodic key changes. Consequently, former employees in such cases can still access and decipher encrypted data.

Illustration of Symmetric Encryption
1 Comment

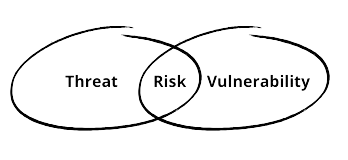
Vulnerability, Threat and Risk

Part of security teams duties is to check their systems, and they need to figure out how someone might try to break in. They would look for weak spots, possible dangers and things that could go wrong.

In this post I’ll speak about difference between Vulnerability, Threat And Risk.

  • Vulnerability is a weakness, or to put it simply, a flaw in a system that could be exploited to breach security. While there’s no such thing as a completely secure system, and we often see Zero-Day exploits (vulnerability before it’s patched) happening, we can at least try to protect our systems by applying the latest patches to firmware and software, as well as properly configuring the system and hardware.
  • Threat is possibility of someone or something exploiting a weakness to breach security,
    whether intentionally or unintentionally. The individual or thing responsible for threat is known as threat actor or threat agent. Attack vector is the pathway or method used by threat actors to breach a network.
  • Risk is the chance of using a weakness to break into a system. We need to assess these risks, which are vulnerabilities we find. Then, we can figure out how likely it is for a bad actor to exploit them and what damage that could cause.

For basic risk assessments, we can use a simple formula:

Risk = (Threat x Vulnerability ) x Impact
Comments closed

Tool for Website Safety and Threat Detection

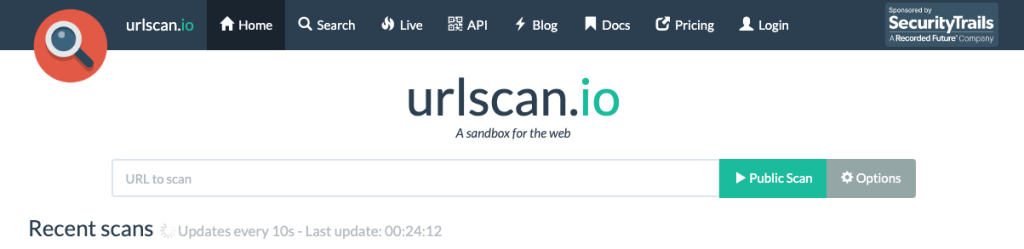
Ever stumbled upon a site that didn’t quite seem right? Whether you’re a cybersecurity enthusiast or just curious about the digital realm, URLScan.io can be a powerful tool for delving deeper. It analyzes websites in detail, examining content, connections, and the technical framework behind the scenes

Think of URLScan.io as a high-powered website scanner. It delves deep, analyzing websites in comprehensive detail, tracing content connections, and unveiling the technical components that keep the site running.

The Benefits of Using URLScan.io

Security Insights: For those eyeing potentially dubious websites, URLScan.io offers a detailed examination to spot security flaws, revealing crucial warnings that could be easily overlooked.

Live Information: Under the ‘Google Safe Browsing’ feature, URLScan.io instantly reveals whether a website is secure or potentially malicious.

Comments closed