What is Strix?
Strix is a public GitHub project whose authors describe it as an open-source AI penetration testing tool. Penetration testing means deliberately probing software for security weaknesses and demonstrating whether they can be exploited. Strix aims to automate that work through AI agents: software workers that use tools to investigate an application and carry out tests.
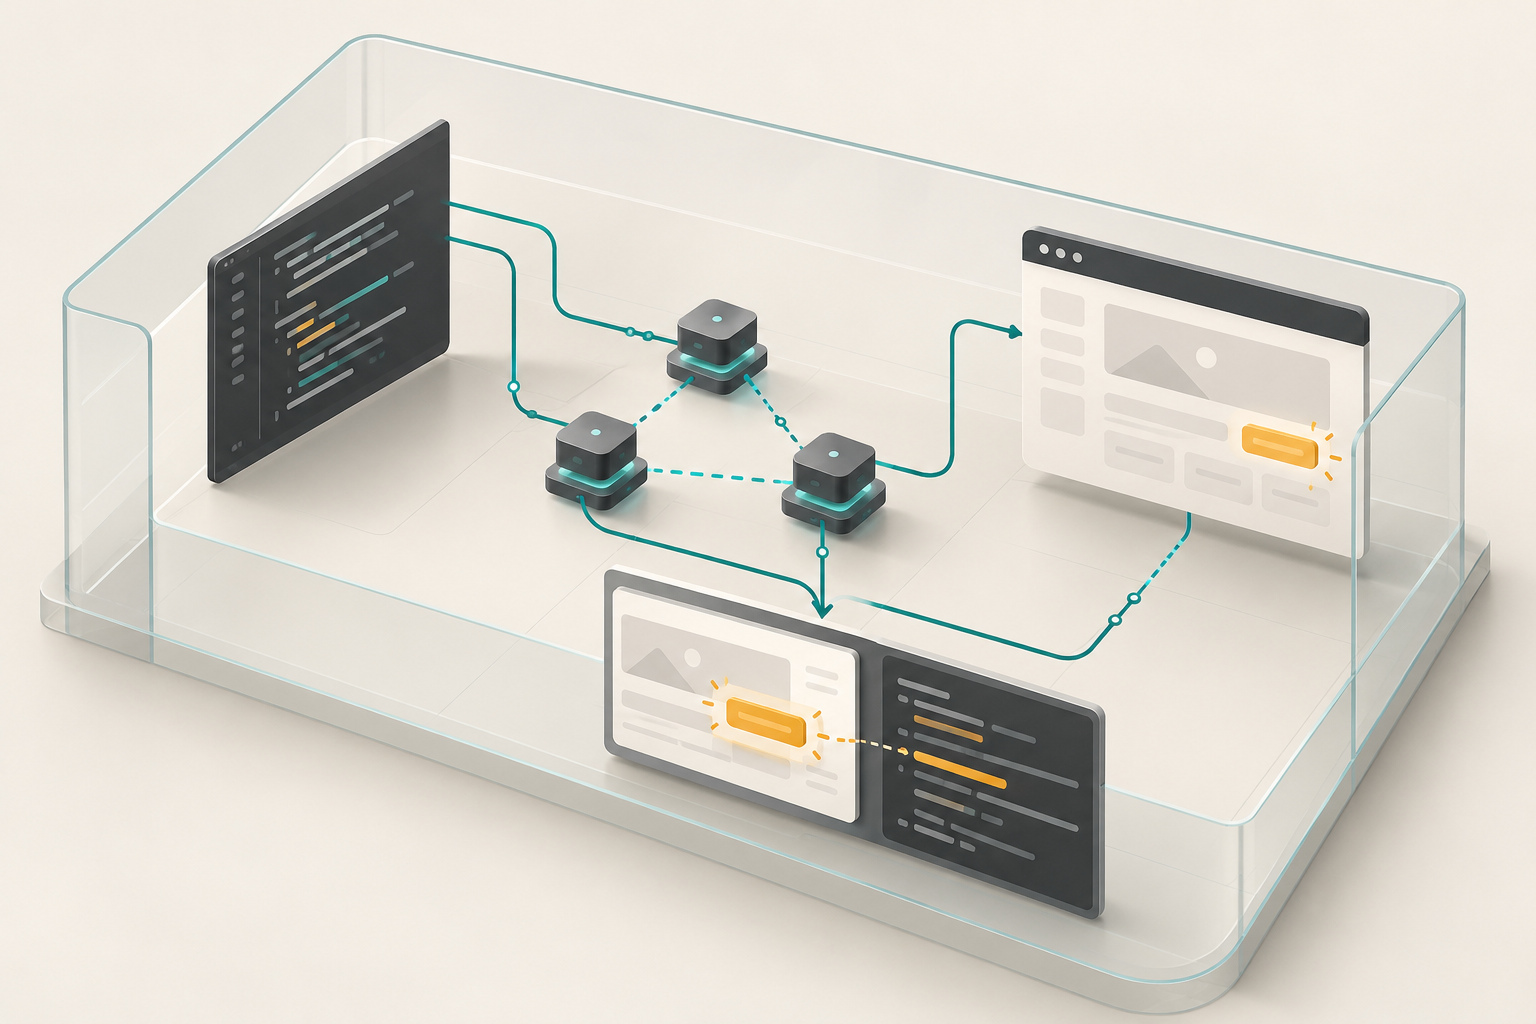
The interesting idea is coordination. Instead of presenting a single automated checker, the documentation describes a team of specialized agents working together. Think of a group of investigators sharing different parts of an investigation: some explore the application, while others investigate weaknesses and validate findings. That is the project’s stated design, rather than an independently established measure of effectiveness.
Looking at code and running applications
The documented capabilities combine static analysis, which examines source code, with dynamic analysis, which examines software while it runs. Strix accepts local code, GitHub repositories and deployed applications as testing targets. Its documentation also describes testing a repository and its deployed application together, bringing those two views into one assessment.
For you as a curious reader, that combination makes the project more interesting than a code-only scanner. Its stated purpose includes observing application behavior and investigating whether a suspected weakness is usable. The documented testing areas include authentication, meaning how an application checks identity, and access control, meaning what an identified user is allowed to access.
Strix’s authors emphasize findings supported by a proof of concept: a working demonstration of a vulnerability. This connects a reported weakness to observable behavior. It describes the evidence the tool aims to produce; it does not establish that every weakness in an application will be found.
What does the project produce?
The documentation lists findings in Markdown, JSON, CSV and SARIF formats. These provide outputs for people to read and for software to process. SARIF is a structured format for security findings; Strix documents it as an output for GitHub code scanning. Local assessments also save run artifacts for subsequent inspection.
The project describes a self-hosted option running on your machine with Docker, a container environment for its testing tools, and your own language-model key—an access credential for the AI model service. A managed cloud service is also documented. For development workflows, the repository describes GitHub Actions integration that can initiate security testing when a proposed code change is submitted for review.
Takeaway
Strix illustrates how AI agents can connect source inspection, application testing and documented evidence. Consider it a project to understand within an explicitly authorized testing scope: its documentation calls for written permission and warns that agents can modify supplied local code, making a clean, disposable checkout a sensible starting point.